Ledger is investigating reports of cryptocurrency losses involving customers in Southeast Asia who purchased hardware wallets through reseller CryptoBilis.
On October 9, 2026, Ledger asked CryptoBilis to temporarily pause sales and shipments while the company investigates the reports.
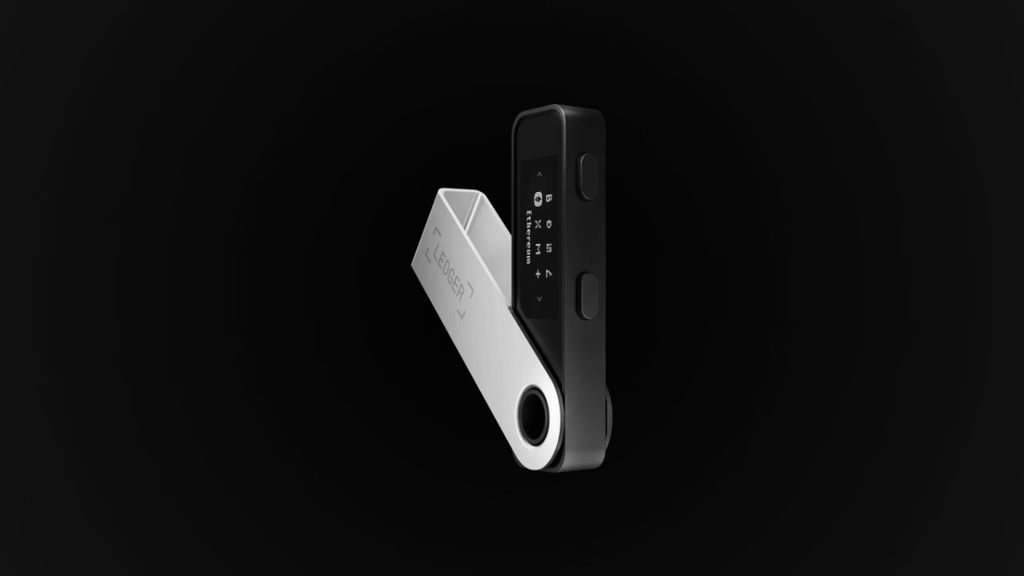
At this stage, Ledger has not confirmed the cause of the losses, nor has it confirmed a vulnerability affecting Ledger devices more broadly.
What Ledger Is Telling Recent Buyers
The warning specifically applies to customers who purchased devices from CryptoBilis within the past 90 days.
Ledger advised users who have not yet initialized their device to avoid setting it up for now.
Customers who already completed setup were advised to consider moving their funds to a new Ledger signer using a newly generated seed phrase.
That distinction is important. Simply replacing the device while restoring the same recovery phrase would keep the same private keys, so users concerned about possible key exposure would need to generate a completely new wallet.
Reports Estimate Nearly $93 Million in Losses
Blockchain analytics company Bitquery published a separate investigation on October 9 estimating that approximately $92.9 million was taken from 311 wallets across several networks.
Bitquery also identified patterns such as closely timed transactions and earlier test activity, which it interpreted as signs of coordinated access to wallet keys.
However, this does not confirm how those keys were obtained, and Ledger has not confirmed that all of the wallets identified by Bitquery are connected to CryptoBilis customers.
No Evidence of a Global Ledger Vulnerability
Ledger has not confirmed that the devices themselves were compromised.
In comments reported by Cointelegraph, the company said the incident appears to be isolated to the reseller and affected market, with no reports involving devices purchased directly from Ledger.
That remains part of the ongoing investigation rather than a final security conclusion.
For now, claims that this represents a vulnerability affecting all Ledger hardware wallets go beyond the evidence currently available.
What CryptoBilis Customers Should Do
If you recently purchased a Ledger device through CryptoBilis, the safest approach is to review Ledger’s official reseller-specific guidance.
Users who have not initialized their wallet should avoid doing so until the investigation provides more clarity.
Those who already initialized a device and are concerned about possible exposure should consider moving assets to a new wallet created with a completely new recovery phrase.
The situation remains under investigation, and the most important distinction is that the reported losses have not yet been linked to a confirmed Ledger hardware vulnerability.
The current warning is specifically connected to customers who purchased devices through CryptoBilis in Southeast Asia.
Until Ledger completes its investigation, users should rely on official guidance and avoid drawing broader conclusions about the security of all Ledger devices.
